

Consumers play a central role in the EU’s digital ecosystem. Special attention must be given to vulnerable consumers, who are often more susceptible to certain online practices. However, safeguarding these individuals must be carefully balanced with protecting overall user privacy. Shifting towards a more dynamic definition of vulnerability risks undermining established EU data protection standards, such as data minimisation.
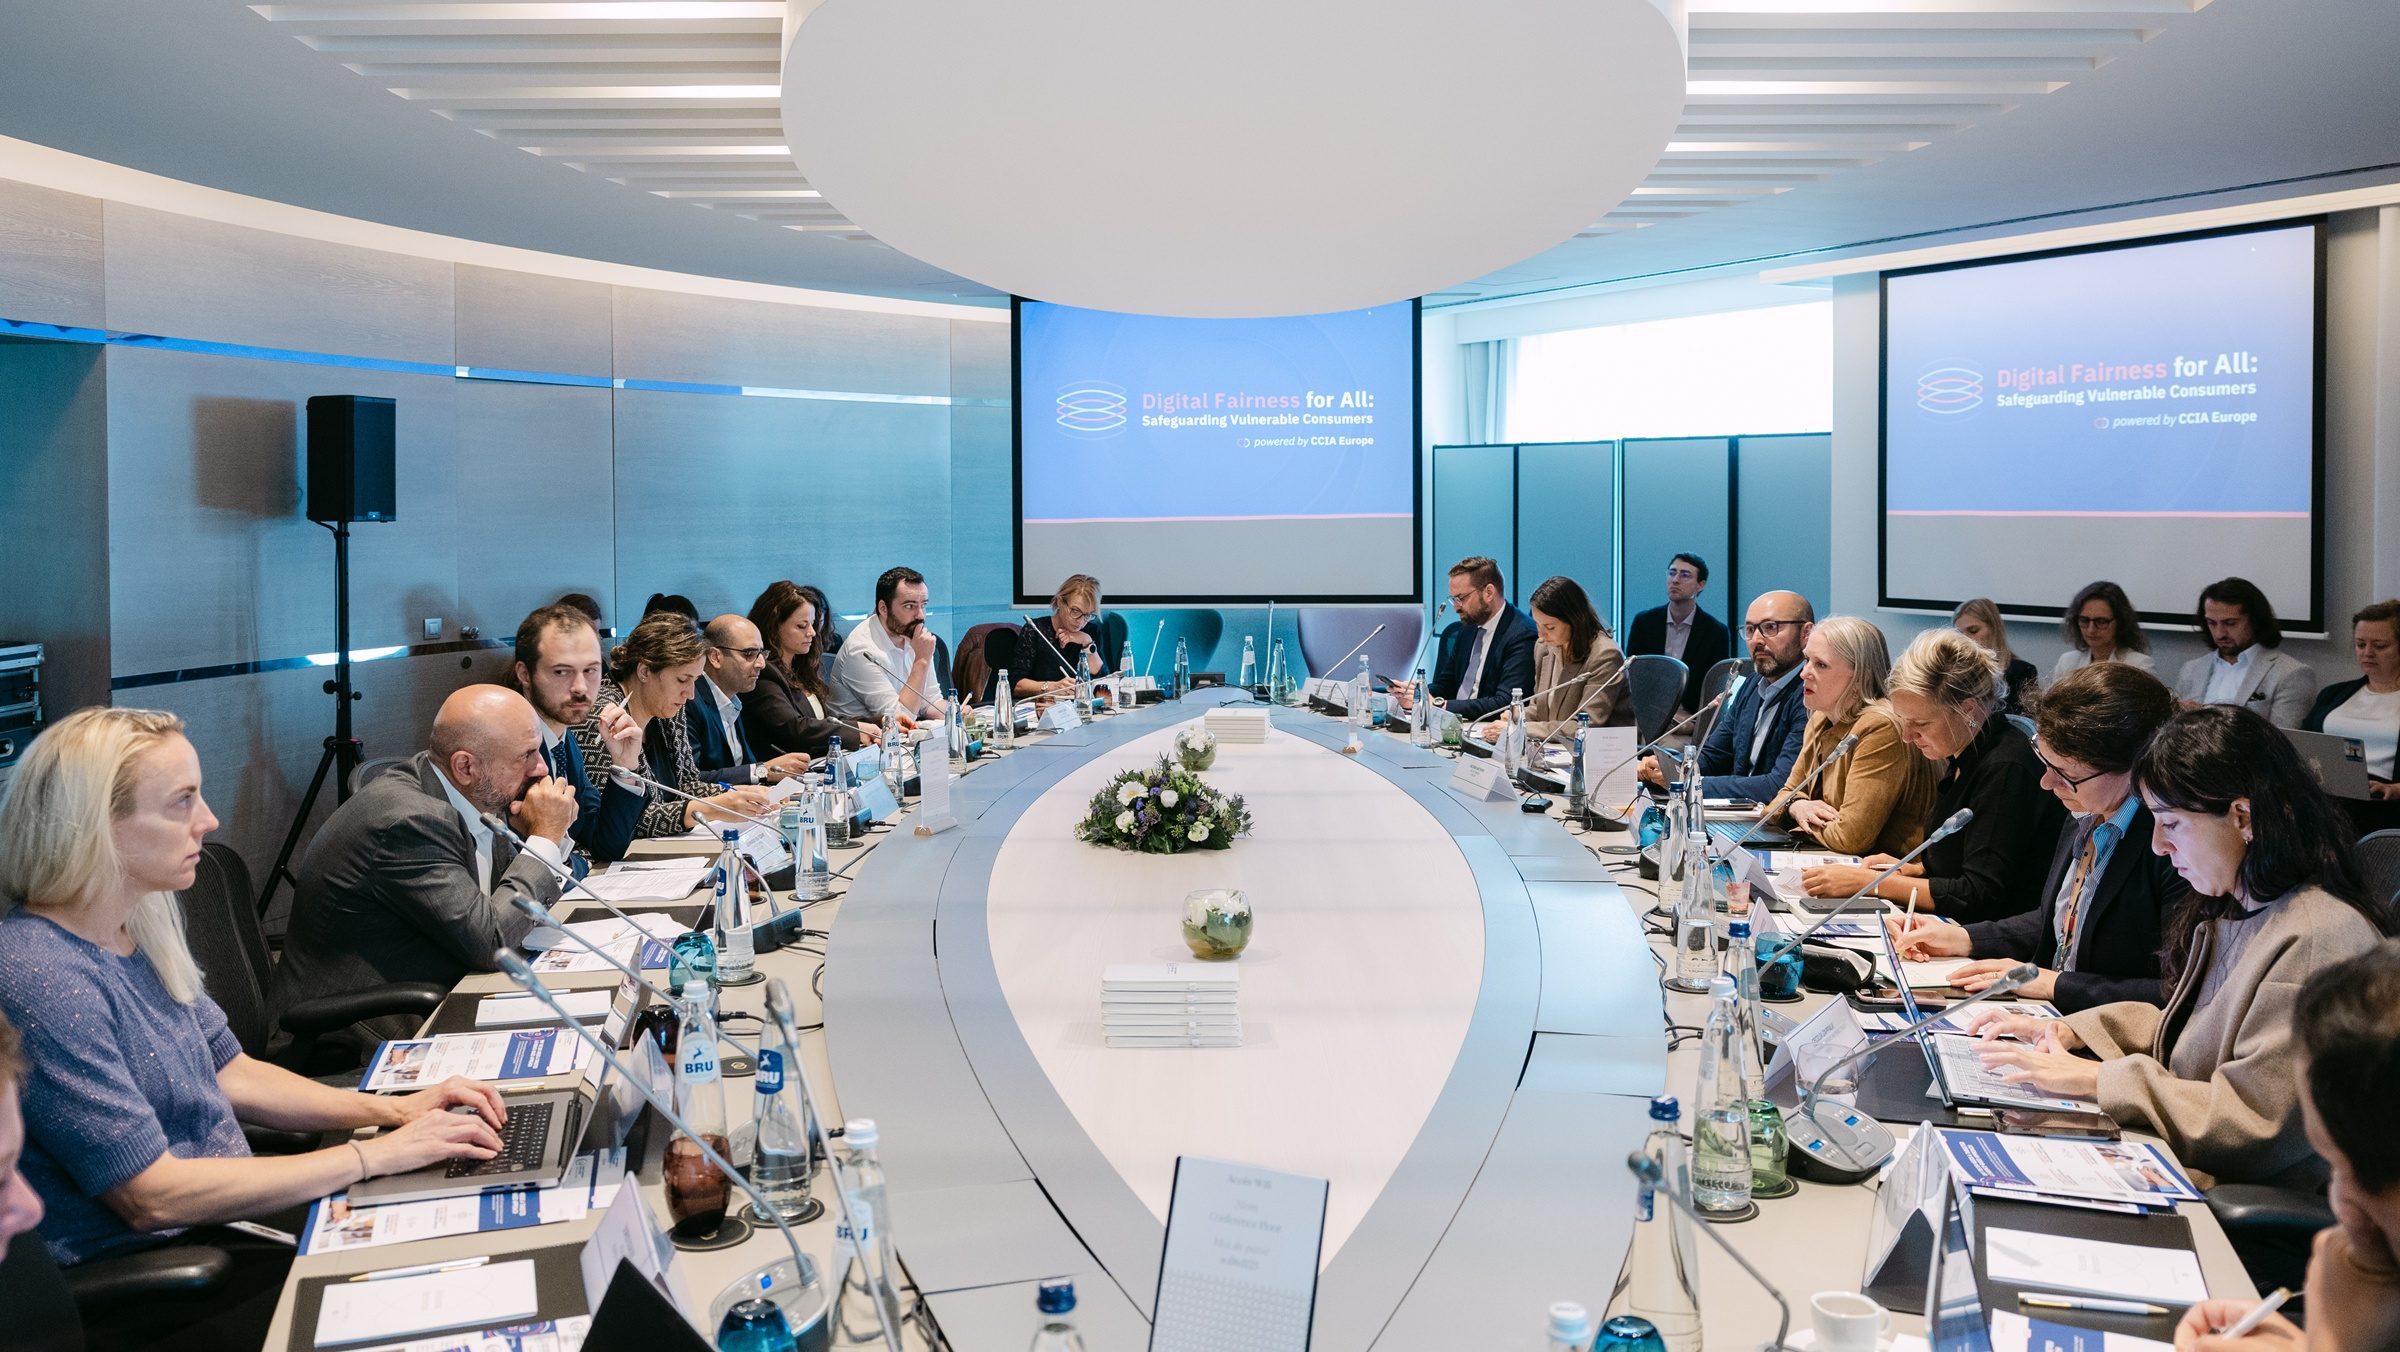
To explore these questions, the Computer & Communications Industry Association (CCIA Europe) convened a roundtable in Brussels on 9 September 2026 to discuss consumer vulnerability and the upcoming Digital Fairness Act (DFA). The discussion brought together policymakers from the European Commission and Member States, consumer organisations, industry experts, think tanks, academics, and other important stakeholders.
Participants explored what consumer vulnerability means in today’s online environment and how to protect vulnerable consumers more effectively without unnecessarily limiting their choice or autonomy. Experts also highlighted the comprehensive safeguards provided by existing EU legislation, including the General Data Protection Regulation (GDPR), Digital Services Act (DSA), and the Unfair Commercial Practices Directive (UCPD). Together, these rules already provide robust protections for consumers, including those who may find themselves in vulnerable circumstances.
As discussions around the DFA continue, participants stressed the importance of ensuring that any new measures should be targeted and proportionate, and fit within a coherent regulatory framework. Indeed, a clear and predictable framework can, in turn, help businesses contribute more effectively to consumer protection online.
This balance is particularly relevant to how vulnerability is defined. Roundtable attendees discussed the challenges of shifting from clear-cut categories towards a more dynamic understanding that takes account of a person’s circumstances and vulnerability to specific issues at particular points in time.
Participants stressed the significant privacy and data protection risks that such an approach could entail. Identifying whether someone may be vulnerable in a particular context would require organisations to collect, infer, or process more information about that person and their circumstances than they do today.
Many attendees agreed that this could sit uneasily with established EU data protection principles, such as data minimisation, and raise questions about the processing of sensitive personal data, including information about someone’s health or sexual orientation.
Participants therefore emphasised the need to consider how future consumer protection measures would interact with existing data protection safeguards, while fully respecting Europeans’ privacy and personal data. For those currently shaping the DFA proposal, this means avoiding obligations that could inadvertently require businesses to collect or infer more sensitive information to identify vulnerability.
Beyond these privacy concerns, the discussion also covered the role of agentic AI in the context of the upcoming DFA, alongside problematic practices such as dark patterns and certain types of influencer marketing. Participants stressed that any new rules would have to consider different business models, the risk of regulatory fragmentation, and the need for legal clarity for companies and consumers alike.
A selection of photos from the event can be viewed below.


